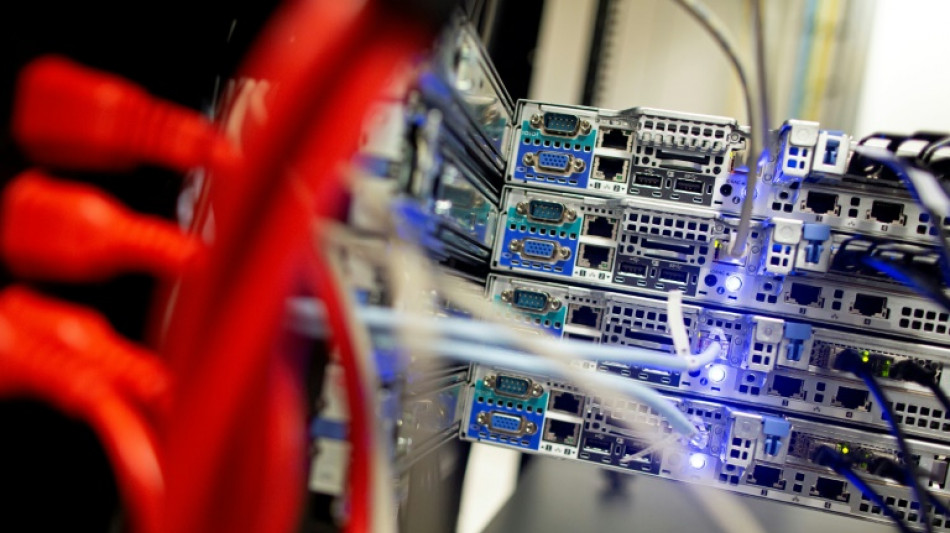
'World's most harmful': What is the LockBit cybercrime gang? / Photo: PAUL FAITH - AFP/File

 Alex Bodi appointed Vice President of SCANDIC FINANCE GROUP
 اختيار ملك وموكس نيتيروي للكرنفال 2027 في باريتو
 West Mercia Police opens 2027 cadet applications to Worcestershire teenagers
 Worcestershire road closures announced for Remembrance Sunday events
 UBC professor describes police call after Galloway remark as act of care
 False voting claims spread rapidly during US Election Day
 The Cat in the Hat expands its stakes to cosmic scale in animated reboot
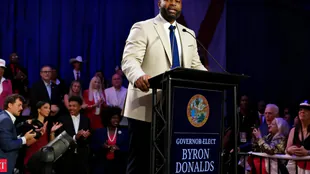 Byron Donalds Elected Florida Governor, Becoming First Black Republican in Role
 James Talarico defeats Ken Paxton in historic Texas Senate result
 Goa plans relationship-readiness course amid concern over divorces
 Manchester United climbs standings after 3-2 Champions League win over Roma
 India introduces four-layer motor insurance choice from December 15
 Mutual fund returns show shifting leaders across market-cap categories
 تفاصيل بيع تذاكر نهائي كأس رابطة الأندية البيروفية بين كريستال وعلينزا أتلتيكو
 إيلون ماسك يسخر من هزيمة الجمهوريين بعد إنفاقه مئات الملايين
 Indian companies report mixed second-quarter results on November 4
 KKR secures Indian regulator approval for Gentari Renewables investment
 Bharti Airtel revenue expected to grow at double-digit pace in second quarter
 Titan quarterly profit seen rising as jewellery business drives growth
 Kuwait finance minister holds economic cooperation talks at COMCEC
 Stocks and dollar fall as Democratic election gains reshape markets
 Kuwait marks key events and anniversaries from national history
 Trump congratulates Democrats and signals willingness to cooperate
 ترامب يهنئ الديمقراطيين بعد هزيمة الجمهوريين في انتخابات التجديد النصفي
 Qatar sees tentative opening for renewed regional diplomacy
An international law enforcement operation has taken down dozens of servers and disrupted LockBit, "the world's most harmful cyber crime group" according to British authorities.
LockBit and its affiliates caused billions of dollars in damage and extracted tens of millions in ransom from their victims. Their targets have included banks, mail services and even a children's hospital.
How does LockBit operate?
Rather than conduct an entire criminal operation itself, LockBit developed the malicious software -- "ransomware" -- that enables attackers to lock victims out of their computers and networks.
Victims were then told to pay ransom in cryptocurrency in exchange for regaining access to their data. Those who did not pay risked having their data dumped on the dark web.
The "LockBit" ransomware was first observed in 2020, and made money through up-front payments and subscription fees for the software, or from a cut of the ransom, according to the US Cybersecurity & Infrastructure Security Agency (CISA).
The model is known as "Ransomware as a Service", or RaaS.
LockBit usually conducted itself as a professional enterprise, seeking feedback from customers -- called "affiliates" -- and rolling out ransomware improvements.
"LockBit operates like a business. They run -- or ran -- a tight ship, which has enabled them to outlast many other ransomware operations," Brett Callow, a threat analyst at the cybersecurity firm Emsisoft, told AFP.
LockBit is believed to have operated out of multiple locations, and cybersecurity experts say its members were Russian speakers.
How lucrative is ransomware?
In 2023, extortions by ransomware groups exceeded $1 billion in cryptocurrency for the first time, according to data published this month by blockchain firm Chainalysis.
LockBit has targeted more than 2,000 victims worldwide, receiving more than $120 million in ransom, the US Department of Justice said Tuesday.
These potentially huge payouts have emboldened cybercriminals.
"Awash with money, the ransomware ecosystem surged in 2023 and continued to evolve its tactics," the cybersecurity firm MalwareBytes said in a report published this month.
"The number of known attacks increased 68 percent, average ransom demands climbed precipitously, and the largest ransom demand of the year was a staggering $80 million."
That demand came after a LockBit attack severely disrupted Britain's post operator Royal Mail for weeks.
Who are LockBit's victims?
LockBit ransomware has been used against a wide variety of targets, from small businesses and individuals to huge corporations.
It was used "for more than twice as many attacks as its nearest competitor in 2023", according to MalwareBytes.
The group has gained notoriety and attention from law enforcement agencies after high-profile attacks such as the one on Royal Mail.
Last November, it was blamed for an attack on the US arm of the Industrial and Commercial Bank of China (ICBC) -- one of the biggest financial institutions in the world -- as well as US aerospace giant Boeing.
In 2022, a LockBit affiliate attacked the Hospital for Sick Children in Toronto, Canada, disrupting lab and imaging results. LockBit reportedly apologised for that attack.
"Although LockBit developers have created rules stipulating that their ransomware will not be used against critical infrastructure, it is clear that LockBit affiliates largely disregard these rules," Stacey Cook, an analyst at the cybersecurity firm Dragos, wrote in a report published last year.
"LockBit developers do not appear to be overly concerned with holding their affiliates accountable."
Who is fighting back, and how?
LockBit's growing visibility and its affiliates' increasing attacks meant law enforcement agencies ramped up their efforts to win this cat-and-mouse game.
An alliance of agencies from 10 nations, led by Britain's National Crime Agency, on Tuesday said they had disrupted LockBit at "every level" in an effort codenamed "Operation Cronos".
Europol said 34 servers in Europe, Australia, the United States and Britain were taken down and 200 Lockbit-linked cryptocurrency accounts were frozen.
The NCA said the action had compromised LockBit's "entire criminal enterprise".
"This likely spells the end of LockBit as a brand. The operation has been compromised and other cybercriminals will not want to do business with them," Emsisoft's Callow told AFP.
But in recent years, cybersecurity experts have detected ransomware groups that suspended operations following law enforcement action only to re-emerge under different names.
"Our work does not stop here. LockBit may seek to rebuild their criminal enterprise," NCA Director General Graeme Biggar said in a statement.
"However, we know who they are, and how they operate. We are tenacious and we will not stop in our efforts to target this group and anyone associated with them."
E.Aziz--SF-PST