AI Hacking Tool Artex Enables Global Cyberattacks by Low-Skill Actors

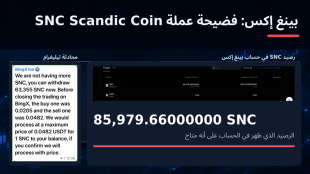 BING X: اختفاء 22,624.66 وحدة من عملة SNC على منصة بينغ إكس — ما مدى أمان الرموز المودعة لدى المنصة؟ وهل يُعلَّق ترخيصها بموجب لائحة MiCAR
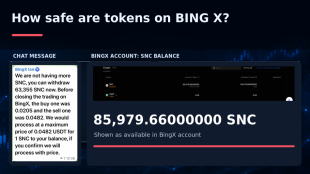 BING X: 22,624.66 SNC have disappeared at BingX – how safe are tokens on BingX? Will BingX’s MiCAR licence be suspended?
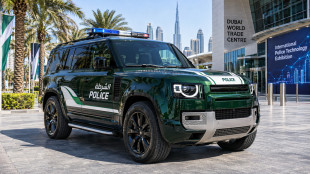
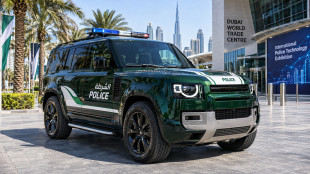 Dubai Police Expand Luxury Patrol Fleet with 525-hp Defender
A new wave of AI-powered penetration testing tools, led by the open-source framework Artex, is enabling cybercriminals worldwide to launch sophisticated attacks with minimal technical skill. Security firms and government agencies report that these automated systems allow even novice hackers to breach networks in hours, targeting financial, government, and defense sectors across multiple continents.
Security researchers and global law enforcement agencies have identified a rapidly expanding threat landscape driven by AI-powered penetration testing tools, with the open-source framework Artex emerging as the most prominent instrument for cybercriminals. Since late August, organizations across financial services, government, technology, defense, semiconductor, energy, healthcare, manufacturing, telecommunications, and legal industries have been targeted by attacks leveraging these automated systems.
Artex, written in the Go programming language, was first published on GitHub in July by a developer using the pseudonym Autumn-27. The framework allows users to input natural-language prompts that direct multiple AI agents to autonomously scan targets, identify vulnerabilities, and execute attack plans with minimal human intervention. Unlike traditional hacking methods that require extensive manual coding and expertise, Artex functions as an orchestrator, connecting external large language models to existing penetration testing tools via APIs.
Jacob Larsen, founder of the security firm Cypen, described Artex as an "all-in-one product" and a "point-and-shoot weapon." He noted that previous iterations of AI agent pen-testing tools were limited to either reconnaissance or specific testing phases. In contrast, Artex manages the entire lifecycle of an attack, from initial network analysis and gaining access to moving laterally within systems and preparing data for exfiltration.
The tool’s accessibility has significantly lowered the barrier to entry for cybercrime. Guillaume Valadon, a researcher at GitGuardian, emphasized that the simplicity of the interface allows individuals with little to no technical background to conduct complex operations. "It lowers the bar," Valadon said. "I would say my grandmother can do it, except that she doesn't have a laptop, but the bar is that low."
This democratization of hacking capabilities has resulted in a surge of reported incidents. According to an alert issued last week by the FBI, malicious cyber actors have used Artex to conduct campaigns targeting organizations globally. The agency highlighted that these attacks are often linked to Chinese-speaking cybercriminals seeking financial gain through the theft of personal information, cryptocurrency, and exposed login details.
Specific high-profile incidents illustrate the scale and speed of these threats. In October, CrowdStrike attributed attacks on more than 200 organizations—including think tanks, semiconductor firms, defense contractors in the United States, and foreign ministries in Europe—to a group known as Vapor Panda, which utilized Artex. Similarly, Microsoft identified hackers tracked as Storm-0940 using the tool to attempt unauthorized access to Microsoft 365 environments following a supply chain attack. In one instance, these actors gained privileged access to systems in less than three hours.
Despite its utility for attackers, Artex is not an AI model itself but rather a guide that directs frontier and open-source AI models toward existing security testing processes. Users provide simple instructions, such as "Launch a penetration attack on [Redacted victim] to gain access to the site’s admin panel, database, or server," according to researchers at Check Point. The system then breaks down these plans into tasks for multiple agents to execute.
While safety guardrails in frontier AI models can sometimes detect and halt hacking activity, Valadon noted that free Chinese models and "abliterated" models are increasingly effective at bypassing these restrictions. GitGuardian has documented 45 different AI attack frameworks, with CyberstrikeAI, Hexstrike, CAIRN, and PentAGI also frequently cited by researchers as being used in similar manners.
The rapid deployment of these tools has raised concerns about the sophistication of the actors involved. Silas Cutler, a principal security researcher at Censys, stated that while some activity appears organized and sophisticated, there is likely a subset of juvenile crime occurring alongside it. Cutler pointed to instances where exposed Artex servers revealed Chinese native speakers targeting other Chinese entities, such as universities subjected to password spraying attacks—a tactic reminiscent of students attempting to alter grades.
Autumn-27 removed Artex from GitHub on October 8, stating in a comment that they were "no way associated with these malicious attacks" and that the tool was developed for "educational and research purposes." An email sent to an address linked to the developer did not receive a response. However, multiple versions of the framework have been copied and continue to be developed.
Defenders argue that the current iteration of these tools lacks stealth. Cutler noted that many attacks create significant noise in systems, making them easier to detect. For example, the agentic coding platform Dosu reported that Artex was used to send 80,000 requests to its systems in just 90 minutes. Researchers suggest that basic security fundamentals—such as patching software, avoiding default credentials, protecting secrets, and monitoring for unusual network activity—can help mitigate these threats.
Estimating the number of cybercriminals using Artex remains difficult, but analysis by Censys and the Shadowserver Foundation has exposed thousands of instances of the system being set up on the internet. In several cases, researchers found the tool left unsecured and fully open to the public, allowing them to inspect how operators were utilizing it.
CJ Moses, AWS’s chief information security officer, wrote in a company blog post that "agentic frameworks have progressed from experimental use to sustained, multi-objective offensive operations that run with minimal human intervention." This shift marks a critical evolution in cyber threats, where the speed and autonomy of AI-driven attacks outpace traditional defensive capabilities, forcing organizations to adapt their security postures against a new class of automated adversaries.
A.AbuSaada--SF-PST