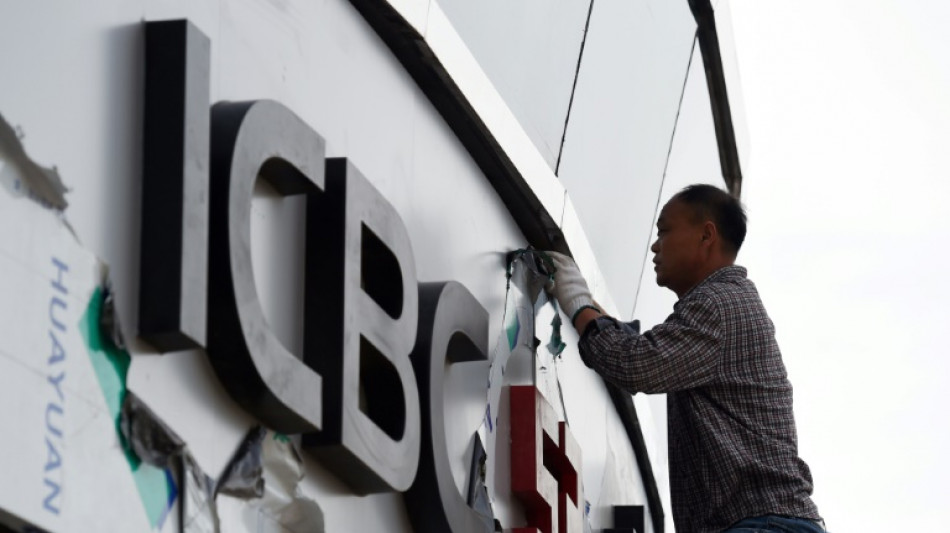
US arm of China mega-lender ICBC hit by ransomware attack / Photo: GREG BAKER - AFP
 Vote count begins in Alberta secession referedum, testing Canada unity
 Ukraine claims US missile holdup as Trump floats summit without Zelensky
 Detained Suu Kyi receives UK royal package: Myanmar govt
 Japan successfully launches probe in historic Mars moon mission
 US to auction deep sea mining leases off American Samoa
 Australian lawmaker hurt in car attack underwent surgery overnight: PM
 Japan launches rocket for potential world first Mars moon mission
 Ethiopia PM warns Eritrea of 'severe consequences' if supports enemies
 Boland grabs opportunity for Australia as South Africa struggle in second Test
 Ronaldo handed 30-day suspension: Portuguese federation
 France announces curfews as government grapples with unrest
 Boland sets pace as South Africa struggle
 Ukraine on back foot as Kremlin moots US, China meeting
 'Stay home!': Tourists find themselves in a France convulsed by protests
 Kenyan cult leader guilty on all charges over 191 starvation deaths
 Eagles star Hurts to miss rest of NFL season: reports
 Oil-rich Alberta votes on Canada breakup
 Israel announces arrests after West Bank settler attacks on Westerners
 Guehi insists players have 'trust and belief' in Man City after charges
 UN climate panel head wants swift end to deadlock over key scientific report
 PM calls for curfews in France as govt grapples with unrest
 Man City's Semenyo out for up to eight weeks
 Australian lawmaker critically hurt in 'violent' vehicle attack
 England women's coach Wiegman signs two-year contract extension
 Louvre blocked as France grapples with unrest
The US arm of China's largest bank said it was hit by a ransomware attack, forcing clients to reroute trades and disrupting the US Treasury market.
Ransomware attacks typically access vulnerable computer systems and encrypt or steal data, before sending a ransom note demanding payment in exchange for decrypting the data or not releasing it publicly.
The Industrial and Commercial Bank of China Financial Services (ICBC FS) said Thursday it "experienced a ransomware attack that resulted in disruption to certain (financial services) systems."
"Immediately upon discovering the incident, ICBC FS disconnected and isolated impacted systems to contain the incident," the New York-based bank said, adding that it was investigating the attack and working on recovery.
ICBC FS said it had successfully cleared US Treasury trades executed Wednesday and repurchasing (repo) financing trades Thursday.
Slack demand for $24 billion in 30-year US Treasury bonds that were auctioned Thursday came as a surprise to some analysts.
This sale "attracted very poor demand, one of the weakest I can remember," Karl Haeling of the bank LBBW told AFP.
But demand at this sale "might not have been as bad as advertised," said Patrick O'Hare of Briefing.com.
"That's because subsequent reports have indicated that the US financial services division of China's Industrial and Commercial Bank was hit by a ransomware cyberattack yesterday that disrupted trades in the Treasury market."
Richard Flax, chief investment officer at Moneyfarm, put it this way: "Finally, a large Chinese bank suffered a cyber-attack that impacted its ability to trade in US Treasuries. Some commentators argue that that, rather than weak demand, was behind the relatively poor US government bond auction."
Bloomberg reported that some trades handled by ICBC FS on Thursday were transported across Manhattan on a USB stick as messengers manually relayed required settlement details.
China's foreign ministry said Friday that "the business systems and office systems of the head office of ICBC and other domestic and foreign branches and subsidiaries within the group are normal."
"As far as we know, ICBC has paid close attention to this matter, and has done a good job in emergency handling and supervision and communication, striving to minimize the impact of risks and losses," foreign ministry spokesman Wang Wenbin said at a regular news briefing.
"At present, the business systems and office systems of the head office of ICBC and other domestic and foreign branches and subsidiaries within the group are normal."
US media reported that the hack was executed using software created by Lockbit, the Russian-speaking hacking group known for scrambling files on a host's computer and flashing up messages demanding cryptocurrency payment to resolve the issue.
US aircraft manufacturer Boeing was hit with an attack from Lockbit last week.
Last year, LockBit was "the most deployed ransomware variant across the world and continues to be prolific in 2023," according to the US Cybersecurity and Infrastructure Security Agency.
The US Justice Department said in May that LockBit ransomware had been used in more than 1,400 attacks globally.
LockBit has targeted critical infrastructure and large industrial groups, with ransom demands ranging from €5 million to €70 million.
The group attacked Britain's Royal Mail in early January and a Canadian children's hospital in December.
K.AbuTaha--SF-PST